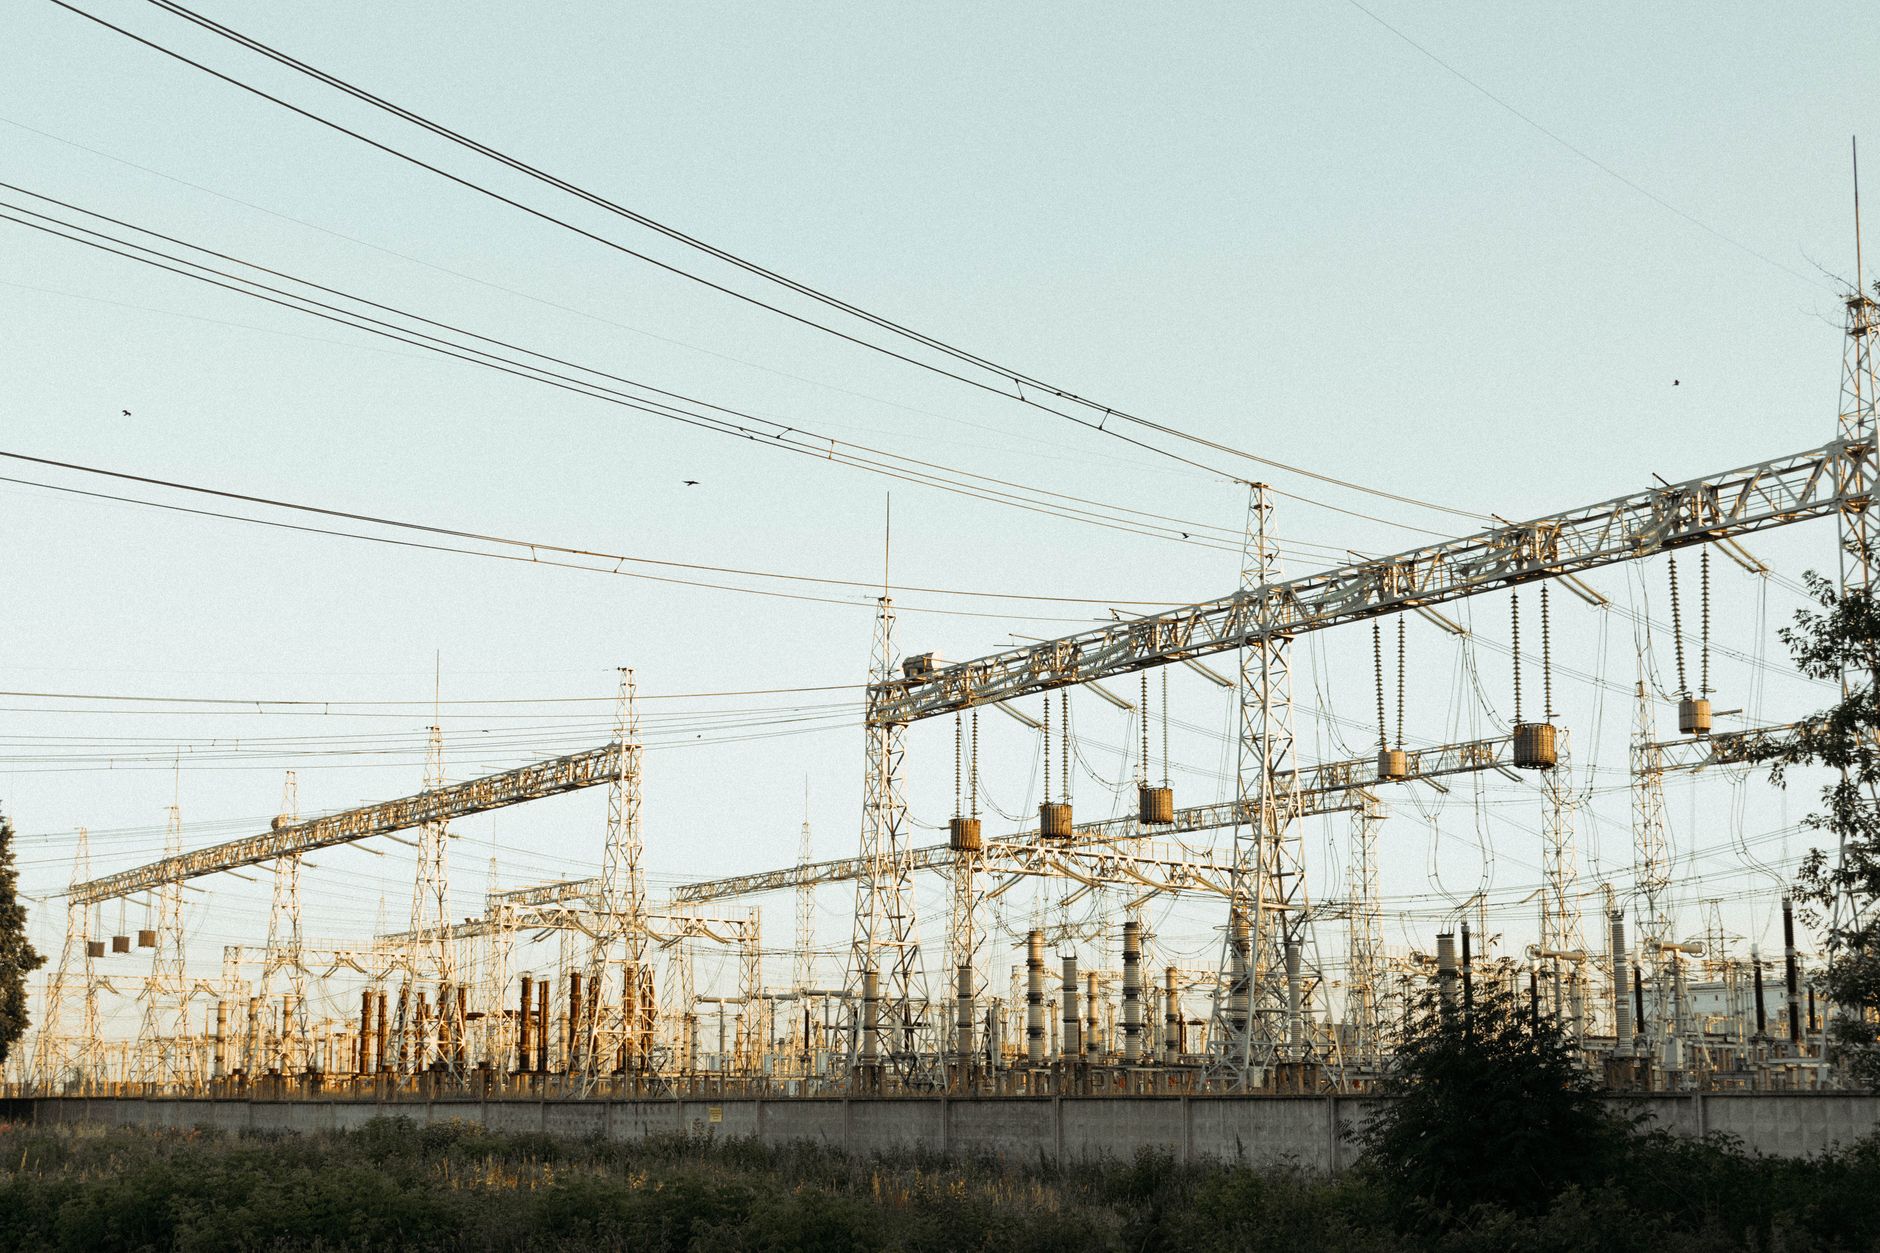
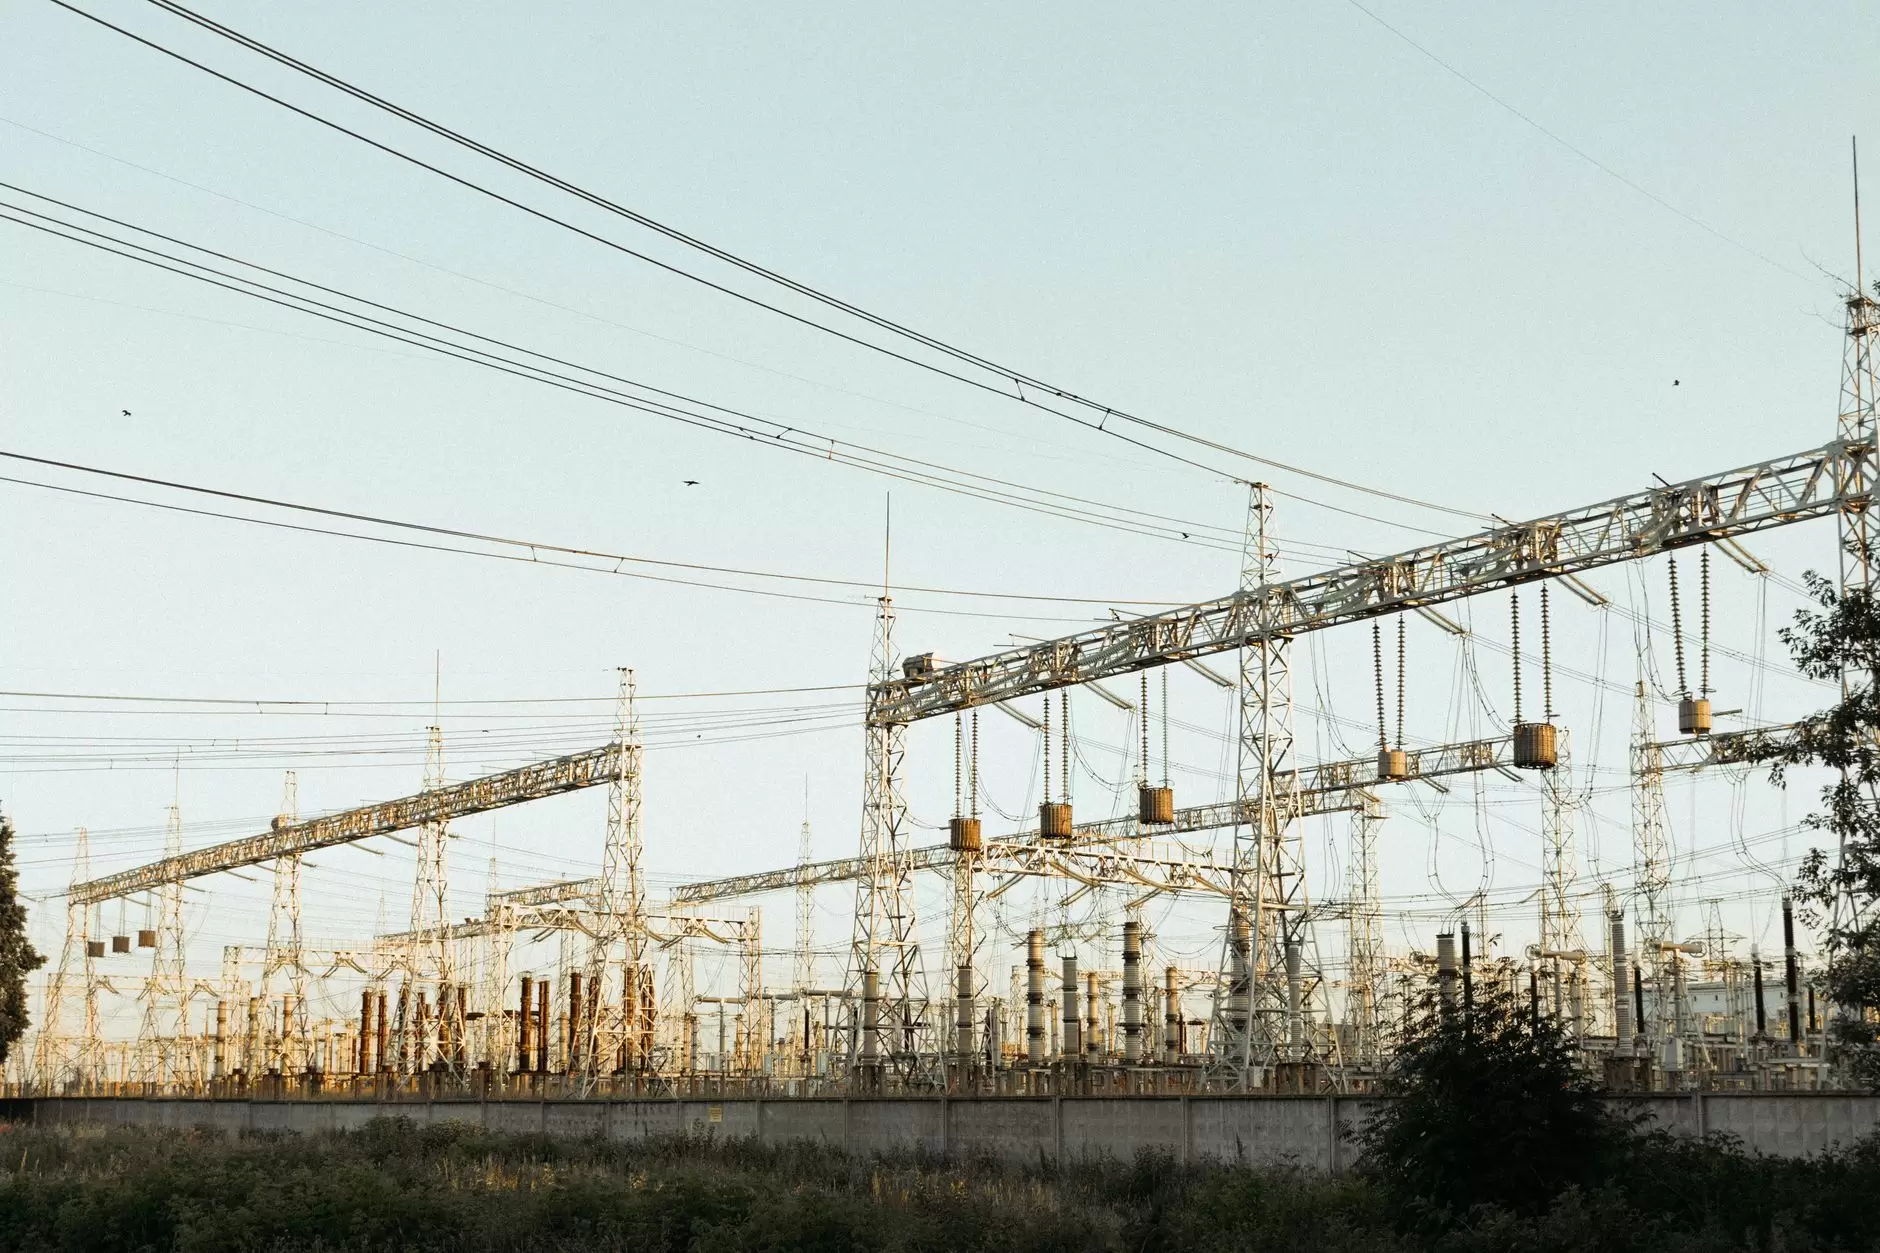
The trip command that clears a fault in a conventional substation travels along a dedicated pair of copper conductors from the protection relay to the breaker coil. That physical path can be verified with a continuity meter, isolated from software configuration, and counted on to work even when other systems fail. For decades, this hard-wired arrangement has been the backbone of power system protection. It is also the part of the station that changes most when a site moves to a digital substation on IEC 61850.
Digital substations replace that fixed physical path with a communication network. The term describes a set of engineering choices around data acquisition, signal distribution, and protection logic, not a single product. At the center is IEC 61850, a standard that defines how substation devices name data, describe capabilities, and exchange the fast messages needed for protection and control. The relevant question concerns how its introduction changes the work of protection engineers, commissioning staff, and operations teams.
Why Copper Reached Its Limit
Hard-wired protection is not failing because copper is fragile. The limitation is the engineering effort required to modify it. When a utility adds a bay to an existing substation, the change extends beyond the new circuit breaker. Protection panels must be re-terminated, drawings updated, and secondary injection tests repeated. Each additional signal requires another conductor across the switchyard. The result is a system that is reliable in its original configuration but becomes progressively harder to extend as the station’s role changes.
That pressure has grown because substations now support functions beyond protection. Power quality monitoring, disturbance recording, asset condition data, and connections to wider grid automation platforms all require data that once stayed local. In a conventional station, each function often has its own wiring, transducer, and interface. The broader grid modernization push has made that fragmentation more visible: utilities now expect operational data from substations to reach control rooms and asset management systems without replicating every signal through parallel circuits. This is a central theme in the wider digital grid conversation around sensors and communication networks.
The cost driver is engineering time rather than materials. Copper and terminal blocks are relatively inexpensive; the hours spent verifying every connection are not. In a brownfield retrofit, a large share of commissioning time can be consumed tracing circuits, checking polarity, and proving that a trip signal reaches exactly one breaker coil. Those labour hours scale with the number of wired points, and the point count grows whenever protection or monitoring requirements expand. A digital architecture does not eliminate that work, but it relocates it from physical verification toward configuration and data management.
How Digital Substations Change Protection and Control
The core idea is to move protection and control signals onto a station communication network built around IEC 61850. In a fully digital arrangement, conventional instrument transformers may be replaced or supplemented by non-conventional transformers that digitize measurements at the source. Merging units publish sampled values—digitised current and voltage measurements—onto a process bus, and protection relays subscribe to those streams rather than reading secondary currents directly. Trip commands travel as GOOSE messages—multicast Ethernet frames used for fast exchange of status and trip signals—over redundant Ethernet links instead of through hard-wired output contacts.
This is more than a change of medium. It shifts the boundary between primary plant and protection system. A relay no longer needs to be physically adjacent to the equipment it protects. Functions can be consolidated, distributed across processors, or virtualized. New protection functions can be added by changing device configuration rather than pulling new cable. The same data stream can serve metering, disturbance recording, and power quality analysis without duplicating sensors. The approach extends the logic described in the article on grid automation, but it moves that automation into the heart of the protection scheme.
In many projects, the transition happens in two layers. A station bus connects protection relays, bay controllers, and the station computer, enabling GOOSE messaging between devices. A process bus extends further into the switchyard, replacing traditional copper circuits to instrument transformers and breakers with digital communications. Utilities can adopt the first without the second, which is why the term digital substation covers a spectrum of configurations rather than a single architecture. That staged path matters because it allows protection engineers to gain experience with data modelling while keeping familiar physical trip circuits in place.
Interoperability depends on standardised data models. IEC 61850 defines how devices name signals, describe their capabilities, and exchange time-critical messages. This is the main difference from older SCADA protocols, which were designed primarily for slower supervisory data rather than protection-grade speed and determinism. In a digital substation, the network itself becomes part of the protection scheme. Its topology, latency, and resilience influence whether a fault is cleared within the intended time. As a result, network design belongs inside the protection engineering scope rather than being treated as a separate supporting activity.
The Trade-Offs Professionals Need to Understand
The shift also changes how utilities think about data boundaries. Substation data must be delivered with deterministic timing. A delayed measurement or lost message can affect protection decisions, not just billing. This distinguishes protection traffic from the consumption profiles generated by smart meters at the customer edge. Smart metering can tolerate less predictable delivery; protection traffic cannot. The communication requirements in a digital substation are therefore more demanding than in many other parts of the digital grid.
One frequently overlooked consequence is the way commissioning changes. In a conventional scheme, a technician can verify a circuit by measuring continuity, injecting a secondary current at one end, and observing the response at the relay. In a digital scheme, the physical path may be absent. Instead, the engineer must confirm that the correct publisher is connected to the correct subscriber, that data types match, and that the configuration corresponds to the intended protection philosophy. A large part of commissioning becomes an information management exercise rather than an electrical verification exercise.
Most sampled-value schemes require time synchronization accurate enough to align measurements from different merging units. A loss of the common time source can degrade protection even if the underlying network continues operating. That makes the time source a central part of the protection scheme, and its failure modes are different from a broken copper conductor that an electrician can identify visually. Some designs reduce the dependency by using fewer merging units or by synchronizing through the network itself, but those choices add complexity to network engineering. This is a trade-off that conventional protection engineers rarely had to evaluate.
Cybersecurity also moves from a peripheral concern to a design requirement. A hard-wired protection scheme has a narrower attack surface, with physical access to equipment or secondary circuits as the principal exposure, although connected control, monitoring, and maintenance interfaces can create additional paths. A networked station offers a larger attack surface, and the same GOOSE messages that enable fast tripping can be manipulated if network segmentation and authentication are weak. Protection engineers now work with information security specialists to define zones, manage access, and plan for network failures without compromising protection speed. This close pairing is one of the reasons the cybersecurity conversation in the digital grid has become so operational.
Where Digital Substation Implementation Is Heading
Fully digital substations remain a minority of installed assets. Many utilities adopt a staged path. They may install IEC 61850-compatible relays and a station bus while retaining conventional instrument transformers and copper trip circuits. This preserves familiar testing methods while introducing standardised data exchange. A smaller number of projects extend the process bus to the switchyard, eliminating most copper between primary plant and protection panels. The choice between these stages is not purely technical.
It depends on the age of the existing station, the expected number of future modifications, the availability of staff trained in network-based testing, and the utility’s tolerance for new failure modes. Greenfield stations with multiple bays or complex protection schemes often justify the move to process bus because the avoided wiring and future flexibility can offset the additional design effort. Brownfield stations are more likely to see a longer hybrid period. A station that has operated reliably for thirty years does not need a process bus to continue doing so; the case for change rests on future requirements, not past performance.
Regional differences also shape adoption. In jurisdictions with high volumes of renewable connections and frequent grid changes, the flexibility of a digital architecture can be more valuable than in stable networks where a substation may remain unchanged for decades. Connection codes and utility specifications vary. Some have begun to reference IEC 61850-based protection interfaces, while others still assume copper-wired trip circuit supervision. These differences mean the transition does not follow a uniform global timeline. One useful way to understand the gap is to compare a new substation built for a single wind farm with a century-old urban transmission station; the protection staff in each face different constraints and see different value in the same architecture.
The more useful question is how supporting practices mature. Testing tools are adapting to handle network traffic alongside secondary injection. Protection settings are now stored as versioned data models rather than as wiring diagrams. Cybersecurity requirements are becoming part of the initial protection design rather than an afterthought. Training programmes are being revised around data modelling and network diagnostics. These changes determine how quickly the technology moves from demonstration projects into standard practice. They also shape whether the digital substation delivers the operational flexibility it promises, or simply replaces one set of engineering constraints with another.
For operating companies, the digital substation does not remove the need to understand protection principles. It changes where those principles are applied. A relay that receives sampled values rather than secondary currents still has to detect the same faults and issue the same trips. What changes is the environment around it: the network, the time source, the configuration process, and the skills needed to keep it healthy. The stations that navigate that change successfully tend to be the ones that treat data engineering as part of protection engineering, rather than as a separate IT project.
References
- IEC 61850 Standard Series — Communication Networks and Systems for Power Utility Automation (substation automation data modelling and messaging architecture)
- IEC 61850-8-1 — Communication Networks and Systems for Power Utility Automation – Part 8-1: Specific Communication Service Mapping (SCSM) – Mappings to MMS (ISO 9506-1 and ISO 9506-2) and to ISO/IEC 8802-3 (defines GOOSE message exchange)
- IEC 61850-9-2 — Communication Networks and Systems for Power Utility Automation – Part 9-2: Specific Communication Service Mapping (SCSM) – Sampled Values over ISO/IEC 8802-3 (defines sampled value transmission)